Hackers get in. SecureSMX keeps them contained.
Attackers are moving on from phishing to an easier target: the unprotected embedded and IoT devices already in the field. SecureSMX divides your firmware into fully isolated partitions on the Arm Cortex-M hardware you already use — so a breach in one partition cannot reach the rest, and your trusted code keeps running with little or no change.
Open Source and Commercial · Built on SMX RTOS, in production since 1989
50 years of embedded systems experience
Once a device is hacked, it’s too late.
What’s the problem?
Attackers are moving on from phishing to unprotected embedded and IoT devices. Every connected device is now a way in — and once one is breached, the damage to your customers and your reputation is already done. Regulators have noticed: the EU’s Cyber Resilience Act will require connected products sold in Europe to be secure by design and kept patched throughout their lives, with severe penalties for falling short.
What’s the solution?
SecureSMX® is a secure RTOS for Arm Cortex-M v7 and v8 microcontrollers. It splits your firmware into fully isolated partitions, so an attacker who gets into one can’t get into the others to steal secrets and cause equipment malfunctions. It is open source, with commercial Licensing and Support available.
How does it fit my product?
Existing designs: move vulnerable code into isolated partitions one module at a time. Your mission-critical code keeps running with little or no change. New designs: start from a partitioned framework so security is built in from day one. Not on SMX? FreeRTOS and ThreadX ports bring your application over. Zephyr coming soon.
Stop patching every CVE at once.
The flood of documented vulnerabilities called “CVEs” in embedded and IoT devices is relentless. Teams that try to fix them all at once ship hasty patches that fail — and teams burn out in the process.
SecureSMX changes the math. Because every module lives in an isolated partition, you can triage each CVE by the importance of the partition it has breached, and take a measured, wait-and-see approach instead of a fire drill. A breached partition can even be swapped for a stand-in while the rest of the device keeps working.
Isolation, engineered in.
The mechanics behind the promise — for the engineers who will build with it.
Isolated partitions
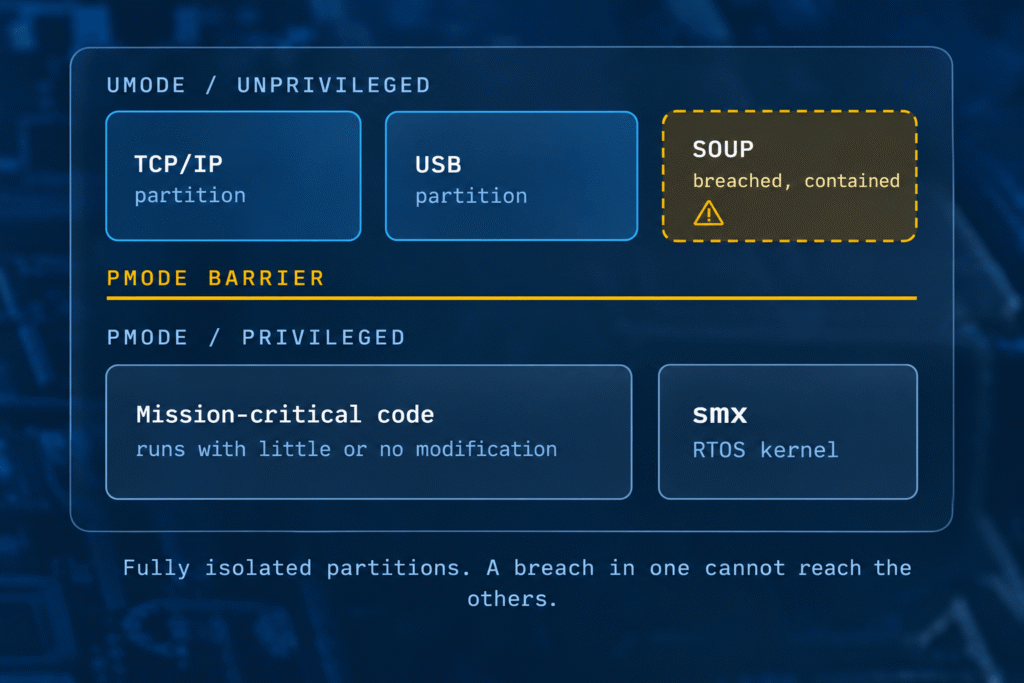
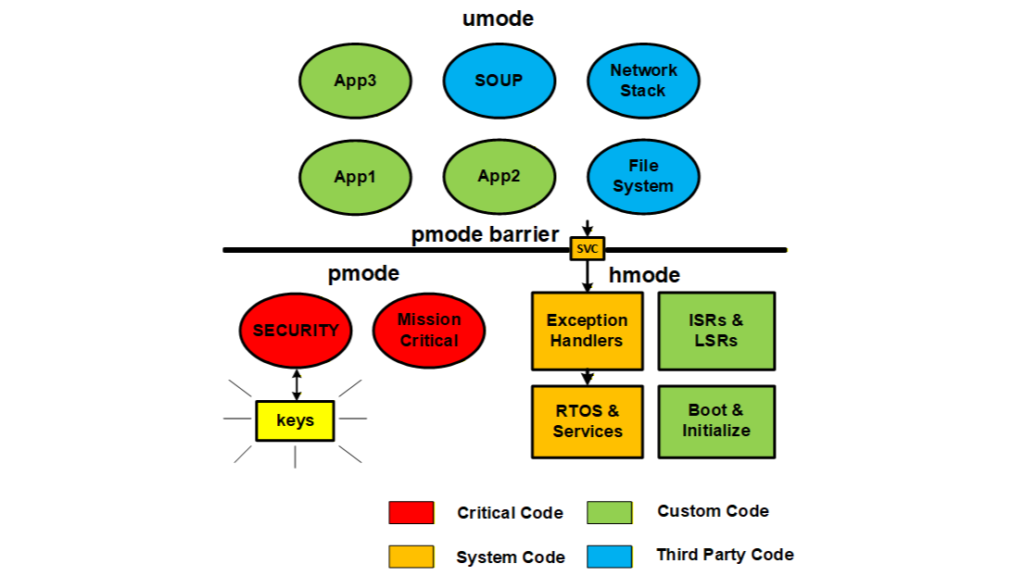
Untrusted code runs in isolated, unprivileged partitions, so a malware breach cannot reach the code or data in any other partition — especially code in privileged mode.
Trusted code runs unchanged
Trusted code needs no modification. It keeps running in privileged mode exactly as it always has, with no rewrite required.
Doubly protected
Trusted code is guarded twice over — by the privileged-mode barrier and by partition isolation. Two independent walls, not one.
Keep running with mock partitions
A breached partition can be shut down and swapped for a mock partition, keeping the main system running until a fix is ready to deploy.
Patch while running
Breached partitions can be updated with patches while the main system keeps running — no full-system downtime to fix a CVE.
Runtime limits and portals
Partitions are held to strict limits so a hacked one can’t exhaust resources or loop forever, and partitions communicate only through standardized portals.
A complete platform underneath.
SecureSMX runs on top of SMX, a full RTOS used in hundreds of devices since 1989, with integrated middleware:
- Multitasking Kernel — The real-time engine at the core, designed for demanding real-time applications.
- TCP/IP — Networking stack for connected embedded systems and IoT devices.
- File I/O — FAT flash file system for reliable embedded storage.
- USB Host / Device — Full USB stacks for host and device operation.
Get on the path to security.
Tell us about your device and we’ll show you how SecureSMX fits it.
Or go straight to the source on GitHub and start building.
Engineers on the other end of the line.
Tell us about your device and where you are with security. You’ll hear back from an engineer, not a salesman.
Technical Support
Support for customers and evaluators working with SecureSMX and SMX.
Sales & Licensing
Pricing, commercial licensing, support contracts, and pre-sales technical questions.
Micro Digital Inc. · Irvine, California · (714) 437-7333
Support, training, consulting, and porting by the developers who wrote the code. SecureSMX on GitHub →